How Forminator Turns a Posted URL Into Executable Shortcode
The exploit targets `/wp-admin/admin-ajax.php` and requires a public Knowledge quiz whose questions are all answered. Forminator's public endpoint supplies the nonce, so that check does not establish a WordPress identity. Version 1.57.2 accepts `current_url`, places it in a social-sharing `data-url` attribute, and escapes it with `esc_url()`. Square brackets remain valid URL characters, so injected shortcode syntax survives. The renderer then sends the entire HTML buffer through `do_shortcode()`, invokes the registered handler, and returns its output in `finalText`. This is arbitrary shortcode execution rather than automatic PHP execution; the final impact depends on the shortcodes registered by the site's plugins and theme.
BitFire FREE Stops Automated Exploit Delivery
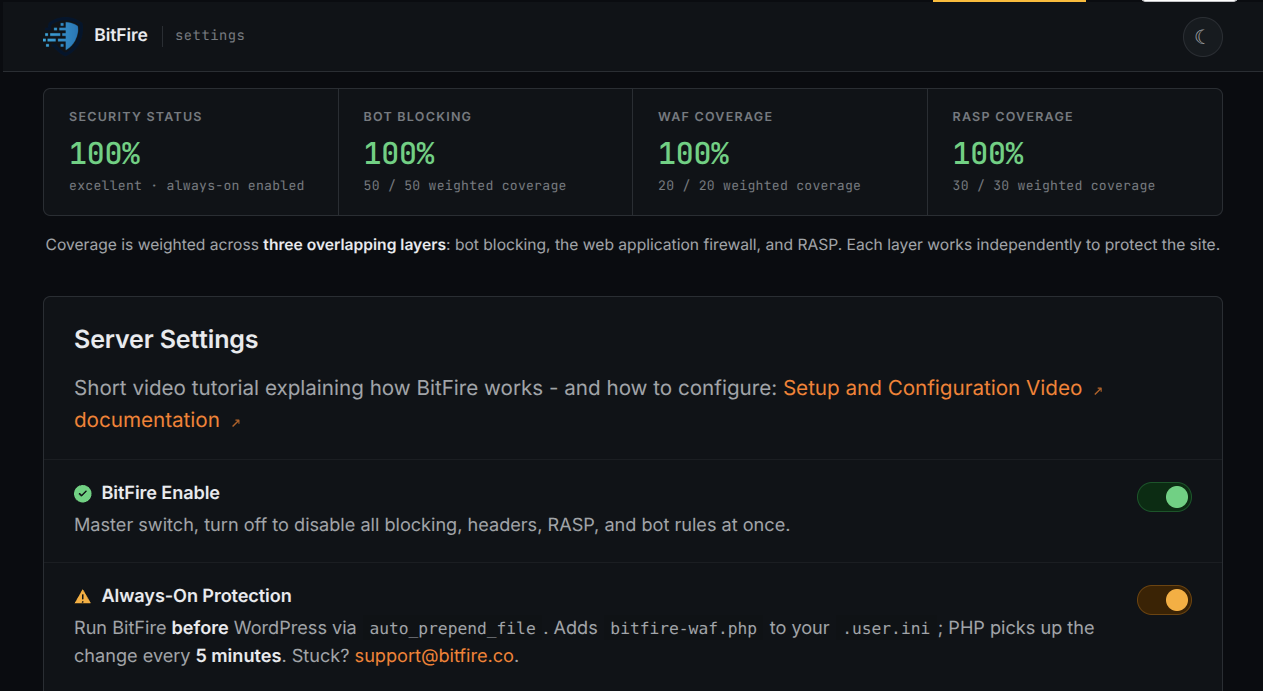
BitFire FREE Bot Protection blocks known attack tools, unknown automated clients, and browsers that have not passed JavaScript verification from submitting the malicious quiz POST. The request is rejected before WordPress dispatches it to Forminator, so the vulnerable renderer never receives the injected `current_url`. Legitimate integrations can be narrowly allowed without disabling other protections. This vulnerability does not require a standard SQL injection, XSS, traversal, or malicious-file payload, so the protection claim does not depend on a WAF signature: Bot Protection stops the automated delivery path itself.
BitFire PRO RASP Blocks Dangerous Shortcode Outcomes
BitFire PRO RASP enforces authorization when WordPress and PHP attempt a protected operation. If an injected shortcode tries to install a plugin or create or modify PHP, filesystem protection denies the unauthorized write before a web shell or backdoor reaches disk. Database protection blocks administrator creation or privilege promotion without administrator authority. Login protection rejects administrator impersonation and authentication-cookie creation when the request lacks valid WordPress credentials. RASP does not sanitize `current_url` or suppress harmless shortcode output; it stops the privileged actions that turn shortcode execution into persistent code or account takeover.
Patch Forminator and Investigate for Persistence
Forminator 1.57.2.1 breaks the exploit twice: it normalizes `current_url` and removes shortcode syntax at the shared input boundary, then processes only trusted administrator-authored text before assembling the result buffer. Update immediately. Patching does not remove an earlier compromise, so sites that exposed a Knowledge quiz on a vulnerable release should investigate before declaring themselves clean. BitFire Threat Hunter can uncover backdoor administrator accounts, hidden database triggers, long-running PHP processes, and droppers that restore malware. Preserve logs, remove discovered persistence, and rotate relevant credentials.
Deploy BitFire's Layered WordPress Protection
BitFire FREE blocks the automated POST before vulnerable Forminator code runs, while BitFire PRO RASP denies unauthorized PHP, plugin, and administrator operations at runtime. Threat Hunter adds the persistence investigation needed after possible exposure. Deploy BitFire, update Forminator to 1.57.2.1 or later, and inspect affected sites for prior compromise. These controls deliver decisive defense before, during, and after exploitation without treating firewall protection as a substitute for patching.