Rules tailored to your site
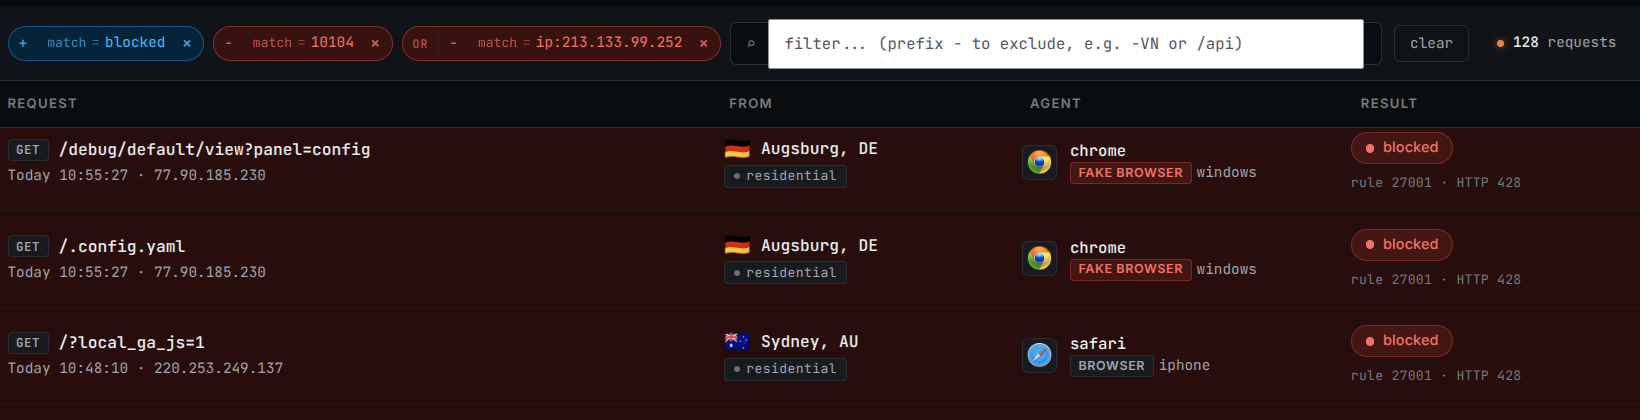
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
Trust the network, not the name →BitFire Pro stops exploited plugins from changing your files, database, or administrator accounts - even when the vulnerability is brand new.
Typical setup: 5 minutes · No credit card required · View Pro runtime controls
BitFire Pro checks protected file, database, and administrator operations inside WordPress, helping stop plugin and theme vulnerabilities before they become site damage.
Explore BitFire Pro runtime controls →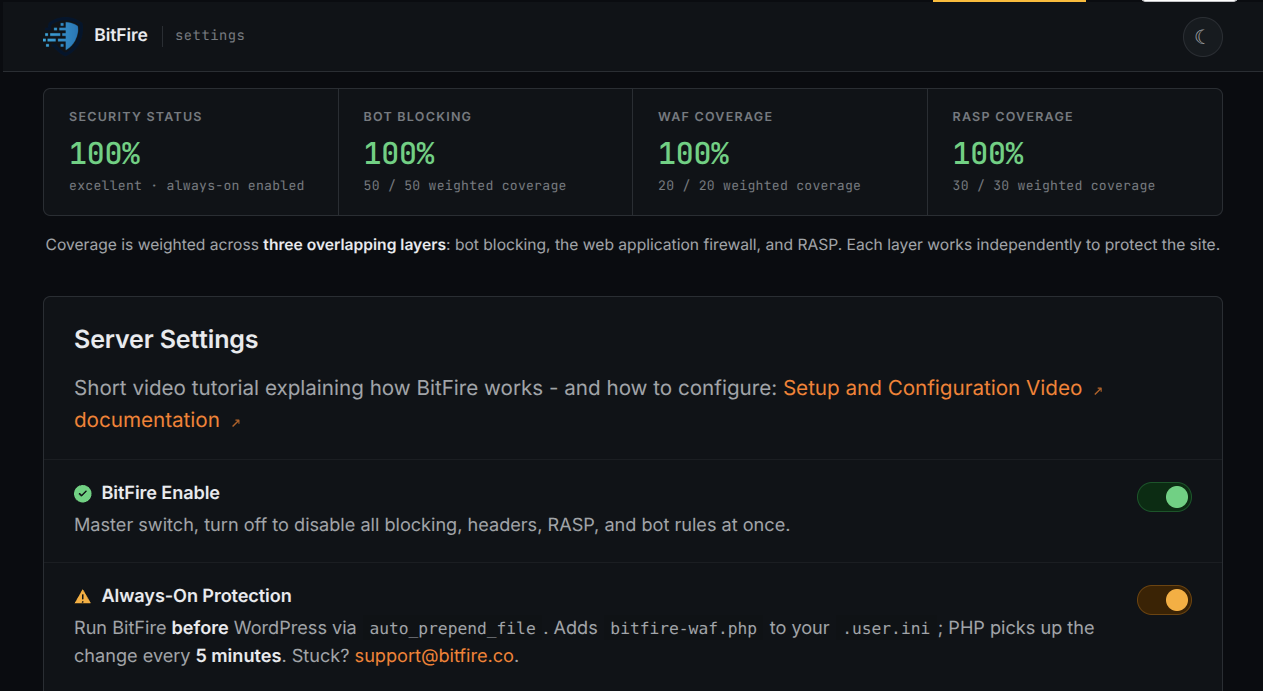
Start with the edge. Add runtime controls where compromise actually happens.
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
Trust the network, not the name →Check authorization for protected PHP writes, database operations, and administrator changes. Coverage depends on enabled controls.
Review runtime controls →Behavioral scanning flags potentially malicious code. AI-assisted analysis helps you review what to allow, repair, or remove. A flag is not proof of infection, and AI analysis can be mistaken. Review evidence and back up files before changes.
Understand why it was flagged →Swipe or scroll across the image; expand for full-size details.
BitFire helps stop real WordPress attack paths before they become file changes, database damage, or administrator takeover.
| Component | CVE and install base | CNA CVSS 3.1 | Assessed BitFire controls |
|---|---|---|---|
| WordPress Double-Decode Template Include | Security advisory technical analysisInstall base: +100,000,000 | 7.1 · High | Bot policy + WAF |
| WordPress Click2Shell | Security advisory technical analysisInstall base: +100,000,000 | 9.3 · Critical |
WAF mitigation + Pro runtime controls in evaluation
Assesses the disclosed theme-preview install chain, the firewall rule deployed against off-site admin-ajax POSTs, and runtime controls still in evaluation. Results depend on client rule deployment and pending PRO RASP hardening. |
| Ninja Forms | CVE-2026-94504 technical analysisInstall base: 500,000+ | 7.2 · High |
Bot policy + WAF + Pro administrator controls
Assesses automated form-submission blocking, stored JavaScript-payload inspection, and unauthorized administrator outcomes. Results depend on client policy, payload shape, and enabled runtime controls. |
Bot policy + WAF
Read analysis : WordPress Double-Decode Template IncludeWAF mitigation + Pro runtime controls in evaluation
Assesses the disclosed theme-preview install chain, the firewall rule deployed against off-site admin-ajax POSTs, and runtime controls still in evaluation. Results depend on client rule deployment and pending PRO RASP hardening.
Read analysis : WordPress Click2ShellBot policy + WAF + Pro administrator controls
Assesses automated form-submission blocking, stored JavaScript-payload inspection, and unauthorized administrator outcomes. Results depend on client policy, payload shape, and enabled runtime controls.
Read analysis : Ninja Forms
“there is only one thing to say: It works! And this is the only firewall [to] realy do the job. In the pro version you [will] get all you need.”Excerpt from the customer’s review.
“The team at BitFire walked us through the entire install process, removed all the malware, and fully protected all our sites. I’ll never run a site without it again.”
Free covers the baseline. Pro is recommended for commercial sites that need protected file, database, and administrator operations checked inside WordPress.
Essential firewall, bot, and malware scan tools for sites that need a simple protection baseline.
Recommended for commercial and business-critical sites that need runtime enforcement, scheduled scanning, and deeper security visibility.
BitFire filters requests, Pro adds runtime checks, and no layer replaces patching, access control, backups, or recovery planning.
Overhead depends on hosting, PHP and plugin activity, enabled controls, traffic, and cache state.
Recommended measurement procedure, not a published test result: use an isolated staging copy, record versions and enabled controls, run the same representative requests, and compare baseline, firewall/bot controls, and Pro runtime controls separately.
Install the free baseline now, or send your site context for a focused technical walkthrough.
Protect my site freeRunning a commercial site? You can start free, but we recommend Pro for runtime controls.